Home › Forums › AWS › AWS Certified DevOps Engineer Professional › Possible Incorrect Answer in Section-Based – Monitoring and Logging (DevOps)
-
Possible Incorrect Answer in Section-Based – Monitoring and Logging (DevOps)
-

A company has confidential files containing patent information stored in an Amazon S3 bucket in the US East (Ohio) region. Among the team members working on the project, actions need to be monitored on the objects, such as PUT, GET, and DELETE operations. The goal is to search and review these actions for auditing purposes easily.
Which solution will meet this requirement MOST cost-effectively?
1. Enable logging on your Amazon S3 bucket to save the access logs on a
separate S3 bucket. Import logs to Amazon OpenSearch service to easily
search and query the logs.2. Enable logging on your S3 bucket. Create an Amazon EventBridge rule that
watches the object-level events of your S3 bucket. Create a target on
the rule to send the event logs to an Amazon CloudWatch Log group. View
and search the logs on CloudWatch Logs.3. Create an AWS CloudTrail trail to track and store your S3 API call logs
in an S3 bucket. Create an AWS Lambda function that logs data events of
your S3 bucket. Trigger this Lambda function using the Amazon
EventBridge rule for every action taken on your S3 objects. View the
logs on the Amazon CloudWatch Logs group.4. Create an Amazon CloudWatch Log group and configure S3 logging to send
object-level events to this log group. View and search the event logs on
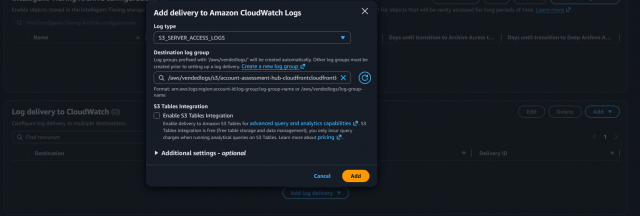
the created CloudWatch log group.I selected 4, but it’s flagged as incorrect. The explanation says:
The option that says: Create an
Amazon CloudWatch Log group and configure S3 logging to send
object-level events to this log group. View and search the event logs on
the created CloudWatch log group is incorrect because you can’t typically configure an S3 bucket to directly send access logs to a CloudWatch log group.However, this does not seem correct. We can configure an S3 bucket to send logs to CloudWatch log group according to this doc
Log in to reply.
